Enterprise Security and Compliance
Trace.Space was designed for regulated industries from the ground up. Not retrofitted for enterprise after the fact. Every deployment mode, every AI feature, every data handling process was built with defense, aerospace, automotive, and medical device security requirements in mind.
Certifications and Data Privacy Standards
SOC 2 Type II
Audited and certified for secure enterprise operations. Controls verified over time, not just at a point-in-time assessment.
ISO 27001
Information security management system aligned with international standards. Systematic approach to managing sensitive company information.
GDPR and CCPA
Full compliance with global data privacy requirements. Customer data protections, data subject rights, and breach notification procedures in place.
Deployment Options: Cloud, VPC, On-Prem, Air-Gapped
Multi-Tenant SaaS
Fully managed infrastructure. Automatic updates, built-in redundancy, SOC 2 certified hosting. SSO integration with Okta, Azure AD, and SAML providers.
Virtual Private Cloud (VPC)
Dedicated infrastructure isolated from other tenants. Data residency controls. Same SSO integration, with additional network isolation guarantees.
On-Premise
Deploy on your own servers, behind your own firewall, under your own security policies. Full control over updates, access, and data handling.
Air-Gapped (Trace.Rack)
Zero external network access. No outside calls. AI inference runs locally on dedicated hardware. Built for programs where data cannot leave the physical building. Trace.Rack ships as a pre-configured hardware deployment ready for air-gapped environments.
AI Data Privacy and Model Control
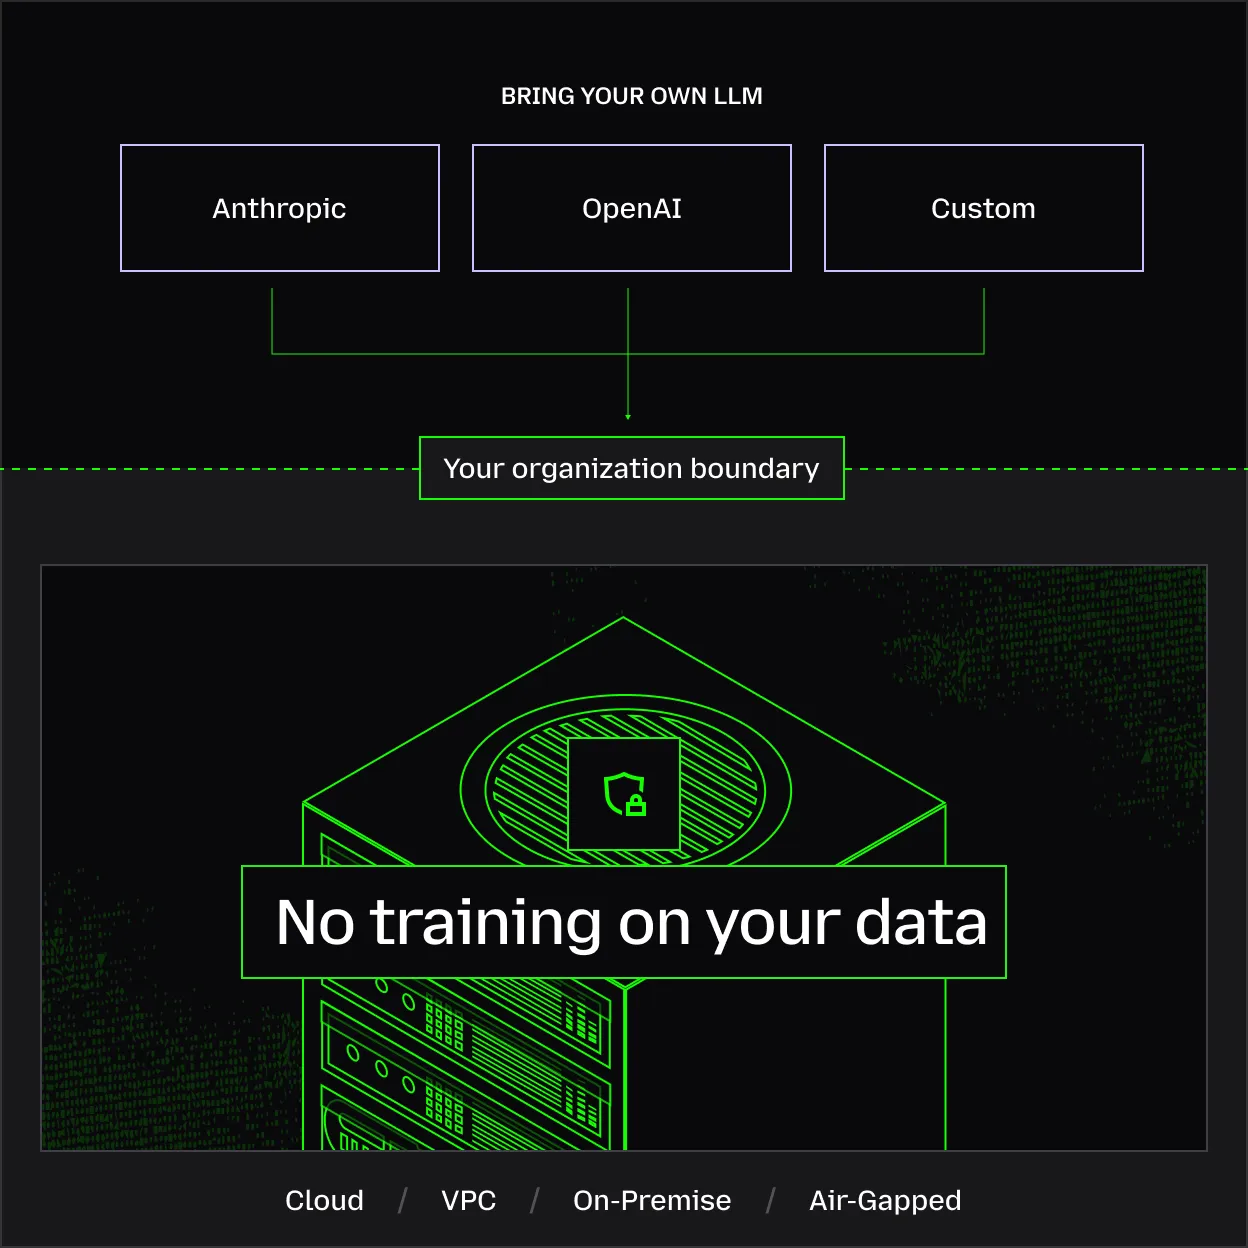
No training on customer data
Customer data is never used to train or improve AI models unless explicitly opted in via written addendum.
Transient inference
Data is not stored, cached, or incorporated into model weights after processing.
Organization-specific embeddings
Embeddings are isolated by design. Never shared across customers. Never accessible outside your organization.
BYOM support
Bring your own LLM keys or connect proprietary model endpoints. You control which AI provider processes your data.
Provider transparency
Trace.Space clearly indicates which AI provider is active at all times. No black-box processing.
Self-hosted control
For on-premise and air-gapped deployments, your organization controls all AI processing. Nothing leaves your environment.
Data Protection, Encryption, and Access Control
Encryption at rest and in transit
AES-256 for stored data. TLS 1.2+ for all communications.
Data isolation
Each customer's data is logically separated with strict access boundaries. No cross-tenant data access.
Role-based access controls
Granular permissions at the project, folder, and item level. Control who can view, edit, review, and approve.
Audit logging
Every action, every access, every change tracked and auditable. Exportable logs for compliance reporting.
Data residency
Choose where your data is stored. Regional deployment options available for organizations with sovereignty requirements.
Regulatory Standards Supported by Industry
Aerospace
DO-178C, DO-254, ARP4754A, AS9100. Audit-ready traceability and coverage analytics that map directly to certification evidence requirements.
Automotive
ISO 26262, ASPICE, ISO 21434. Structured requirements, verification tracking, and process evidence built into daily engineering workflows.
Medical Devices
IEC 62304, ISO 13485, ISO 14971, FDA 21 CFR Part 820. Risk traceability, baseline versioning, and design history file support.
Defense
MIL-STD-961, MIL-STD-881, NIST SP 800-53. Air-gapped deployment, data sovereignty, and access controls that meet the highest classification requirements.
Industrial
IEC 61508, ISO 13849. Functional safety traceability from hazard analysis through verification.
Frequently Asked Questions
What’s the difference between Trace.Space’s VPC and on-premise deployment?

Trace.Space’s VPC deployment runs on dedicated infrastructure isolated from other tenants, with data residency controls, the same SSO integration as the SaaS option, and added network isolation guarantees. The on-premise deployment runs on your own servers, behind your own firewall and under your own security policies, so your team controls updates, access, and data handling. If data can’t leave your building, Trace.Rack adds an air-gapped option, with AI inference running locally on dedicated hardware.
How do SOC 2 Type II and ISO 27001 differ for Trace.Space?
SOC 2 Type II and ISO 27001 differ in kind: SOC 2 Type II is a SOC 2 examination that a CPA performs, and ISO/IEC 27001 is the international standard that sets requirements for an information security management system. Trace.Space is audited for SOC 2 Type II, and its controls were verified over time in addition to a point-in-time assessment. Its information security management system is aligned with ISO 27001.
Which security controls protect requirements data in Trace.Space?
Trace.Space protects requirements data with AES-256 encryption at rest, TLS 1.2+ for all communications, and logical separation of each customer’s data with strict access boundaries and no cross-tenant data access. Role-based access controls set who can view, edit, review, and approve at the project, folder, and item level. Audit logging tracks every action, access, and change, and you can export the logs for compliance reporting.
Does Trace.Space use customer data to train its AI models?
No, Trace.Space doesn’t use customer data to train or improve AI models unless your organization opts in through a written addendum. Inference is transient, so your data isn’t stored, cached, or added to model weights after processing, and embeddings stay isolated to your organization. You can bring your own LLM keys or connect your own proprietary model endpoints, and in on-premise and air-gapped deployments your organization controls all AI processing, with nothing leaving your environment.
How does Trace.Space handle data residency requirements?
Trace.Space handles data residency by letting you choose where your data is stored, with regional deployment options for organizations that have sovereignty requirements. The VPC deployment adds data residency controls on dedicated infrastructure isolated from other tenants. When data must stay on your own servers, Trace.Space runs on-premise, or air-gapped through Trace.Rack for programs where data can’t leave the building.
Your Security Team Will Have Questions. We Have Answers.
Request a security review. We will walk your team through our architecture, certifications, and deployment options.